Security research

Manual SaaS and API security research

Findings and methods from real testing. Access control, APIs, GraphQL, authentication, business logic and AI application security, written so an engineer can act on them.

16 articles8 topicsUpdated 26 September 2026

16 articles

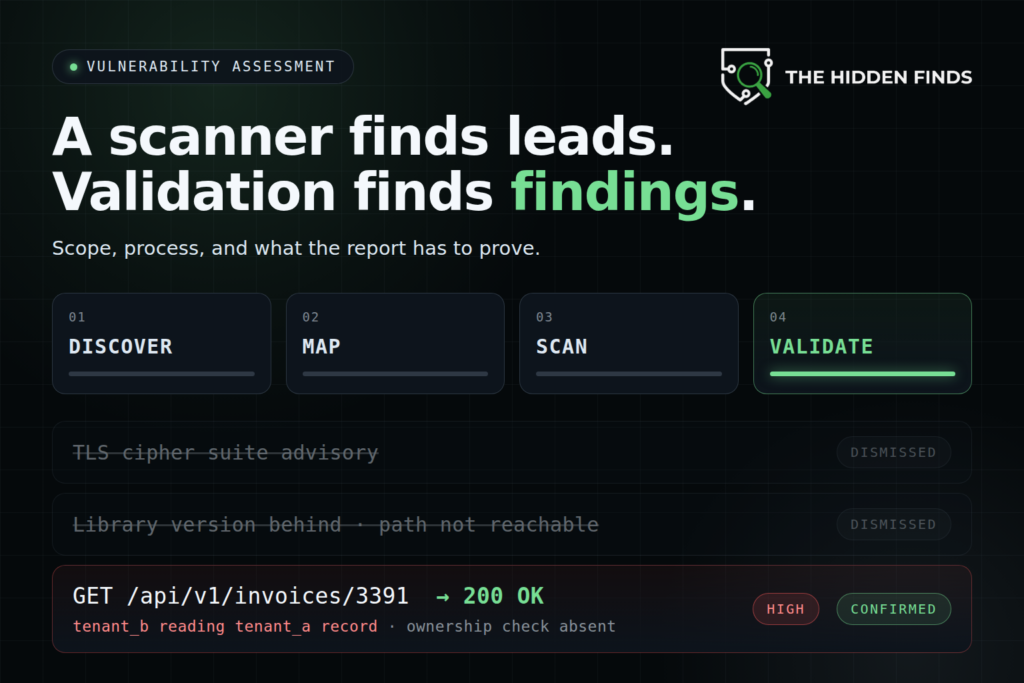
Four stage vulnerability assessment process with two dismissed scanner results and one confirmed high severity tenant isolation finding.Practitioner
Latest
Pentesting Guides13 min read

What Is a Vulnerability Assessment? Scope, Process and What the Output Should Tell You

A vulnerability assessment is a structured review of an application, its APIs and its exposed infrastructure that identifies security weaknesses, confirms which of them are real, and rates each one by the risk it presents to the business. It answers a narrow question well: what is currently wrong, where, and how serious is it. That\u{2026}
All articles

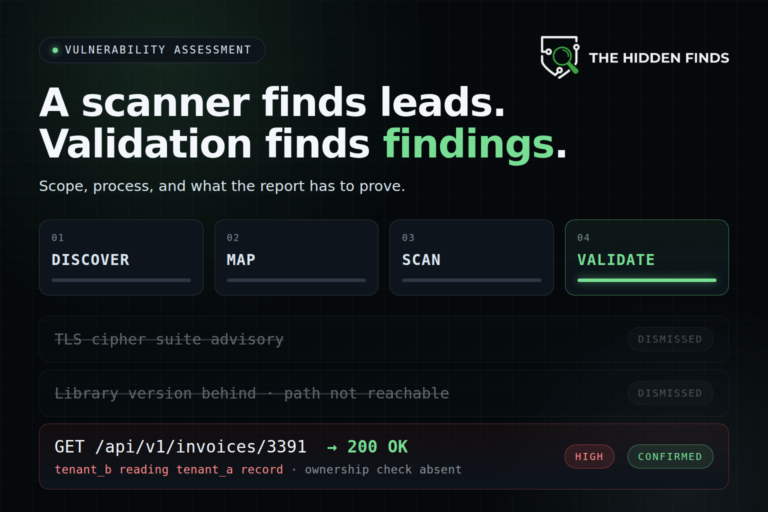
Four stage vulnerability assessment process with two dismissed scanner results and one confirmed high severity tenant isolation finding.Practitioner
Pentesting Guides13 min read

What Is a Vulnerability Assessment? Scope, Process and What the Output Should Tell You

A vulnerability assessment is a structured review of an application, its APIs and its exposed infrastructure that identifies security weaknesses, confirms which of them are real, and rates each one by the risk it presents to the business. It answers a narrow question well: what is currently wrong, where, and how serious is it. That\u{2026}
Key takeawayWhat the scope should cover, what manual validation adds that a scanner cannot, and how to judge the report you get back.
Title card: Penetration Testing Standards, PTES, OWASP and NIST compared. Three standards documents behind one showing an application finding, with a magnifying glass over a 200 OK response returned to the wrong tenant.Practitioner
Pentesting Guides7 min read

Penetration Testing Methodologies and Standards: What PTES, OWASP and NIST Actually Cover

A standard tells you what to test. It does not tell you where your product breaks. This is what PTES, OWASP WSTG, the OWASP API Security Top 10, OWASP ASVS and NIST SP 800-115 actually cover, which parts matter when the target is a SaaS application or an API, and which parts exist mainly so\u{2026}

Key takeawayWhich parts of PTES, WSTG, ASVS and NIST earn their place in a real engagement, and which exist so a report can cite something.
Title card: AI Agents Are Becoming a New Attack Surface. A robot inside a green shield, linked to database, code, cloud and lock iconsDeep dive
AI Security10 min read

AI Agents Are Becoming a New Attack Surface: What SaaS Companies Need to Secure Before Giving Them Access

For years, application security teams have asked a familiar question: What can this user access? That question still matters. But as AI agents become integrated into SaaS platforms, companies increasingly need to ask another one: What can this AI agent access, and what can it do with that access? That distinction is becoming important. AI\u{2026}

Key takeawayAn agent with tools is a user with credentials, so the dangerous combination is access plus autonomy rather than the model itself.
Title card: Business Logic Vulnerabilities. An app workflow of user, cart, team and document steps leading to a cracked shield with a warning signPractitioner
Business Logic5 min read

Business Logic Vulnerabilities: The Security Risk Automated Scanners Miss

Modern SaaS applications are built around business processes rather than simple web pages. Users create projects, invite teammates, purchase subscriptions, approve invoices, generate reports, and collaborate across organizations. Every one of these actions follows a set of business rules that determine what should and should not happen. Most security discussions focus on familiar vulnerabilities like\u{2026}

Key takeawayScanners cannot find these because nothing is malformed. The request is valid and the rule behind it is wrong.
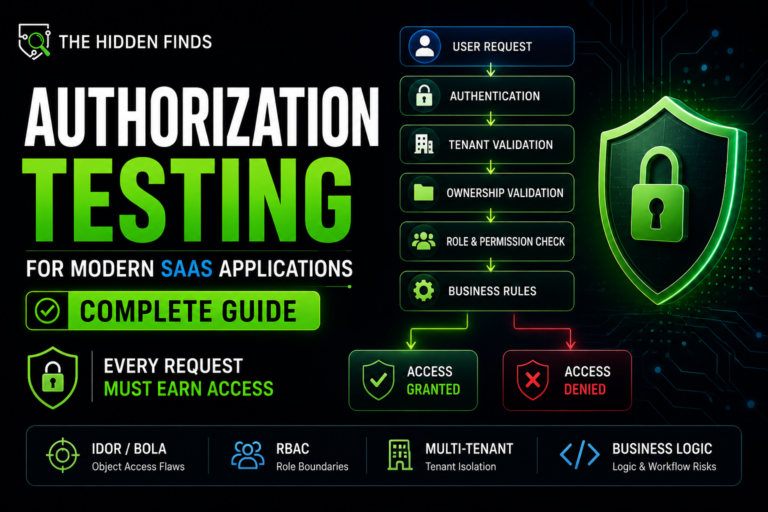
Title card: Authorization Testing for Modern SaaS Applications. A request passes authentication, tenant, ownership and role checks before access is granted or deniedDeep dive
Access Control12 min read

Authorization Testing in Modern SaaS Applications: A Complete Guide

Learn how modern SaaS teams evaluate authorization, role boundaries, tenant isolation, object ownership, and business logic to identify security weaknesses before they become production incidents. Modern SaaS applications are designed to handle some of an organization’s most valuable assets. Customer records, invoices, source code, financial information, healthcare data, internal documentation, AI workflows, and administrative controls\u{2026}

Key takeawayHow to test role boundaries, tenant isolation and object ownership as separate problems instead of one permissions check.
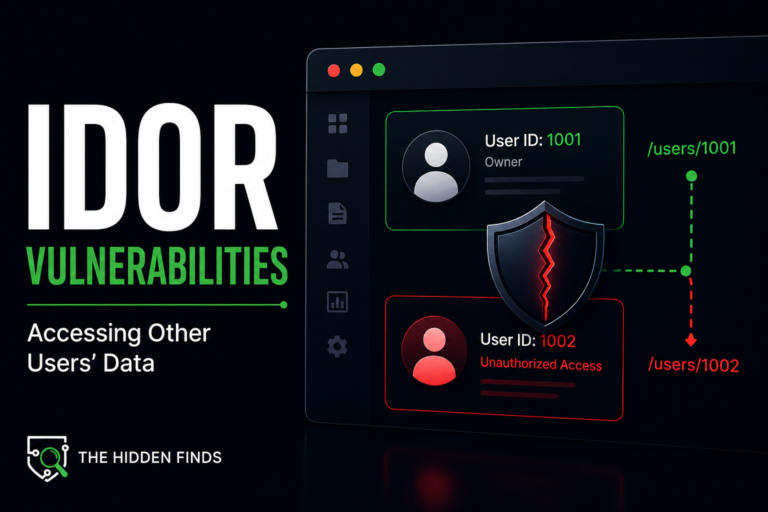
Title card: IDOR Vulnerabilities. The owner of /users/1001 requests /users/1002 and reaches another user's record, marked Unauthorized AccessFundamentals
Access Control8 min read

IDOR Vulnerabilities Explained: How Attackers Access Other Users’ Data

Understanding one of the most common and dangerous security flaws affecting modern SaaS applications. Modern SaaS applications are built around one simple idea: users should only be able to access the data and functionality they are authorized to use. Customers trust these platforms with invoices, customer records, financial information, source code, medical records, and countless\u{2026}

Key takeawayWhy a 200 response to someone else's object ID is the most common serious flaw in SaaS, and how it gets found.
Title card: Broken Access Control. A cracked padlock on a shield, with a red path from an outside user and a GET /api/users/123 request logPractitioner
Access Control7 min read

Broken Access Control: The Security Flaw Behind Some of the Most Serious SaaS Breaches

Most organizations spend a significant amount of time thinking about authentication. They implement strong password policies, enable multi-factor authentication, and invest in secure login systems. These are important controls and should never be ignored. However, many of the most damaging security incidents do not happen because an attacker bypasses authentication. They happen because the attacker\u{2026}

Key takeawayStrong authentication tells you who someone is. It says nothing about what they should reach once they are inside.
Title card: GraphQL Security Risks Every SaaS Company Should Understand. The purple GraphQL logo behind a cracked shield and padlockPractitioner
API Security8 min read

Common GraphQL Security Risks in SaaS Applications

GraphQL has become one of the most popular technologies for building modern APIs. Many SaaS companies adopt GraphQL because it gives developers greater flexibility, reduces over-fetching, and allows applications to retrieve exactly the data they need through a single endpoint. For engineering teams, this often results in faster development cycles and a more efficient frontend\u{2026}

Key takeawayIntrospection, aliasing, batching and query depth each widen the surface in ways a REST focused test never touches.
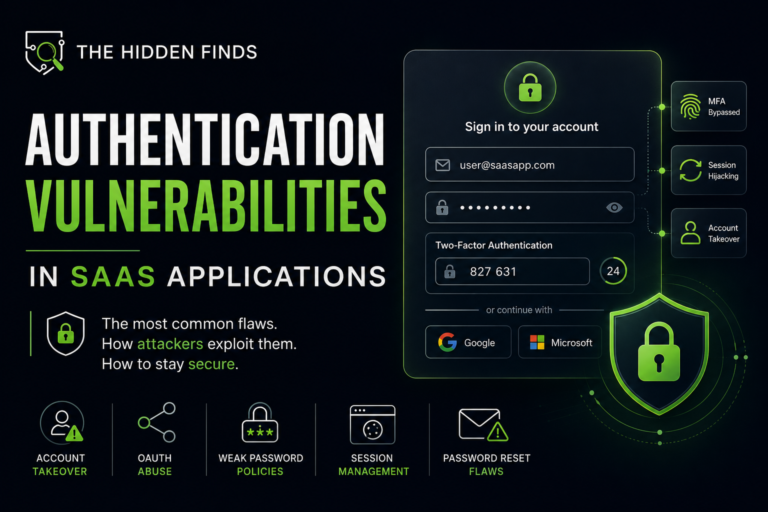
Title card: Authentication Vulnerabilities in SaaS Applications. A sign in form with a two factor code, flagged for MFA bypass, session hijacking and account takeoverPractitioner
Authentication7 min read

The Most Common Authentication Vulnerabilities in SaaS Applications

Authentication is one of the most important security controls in any SaaS application. It verifies that a user is who they claim to be, and establishes the identity that every later access decision depends on. Every login page, mobile application, API, and third-party integration ultimately relies on authentication to establish trust between users and the\u{2026}

Key takeawayWhere MFA, OAuth, session handling and password reset actually break, beyond credential stuffing and weak passwords.
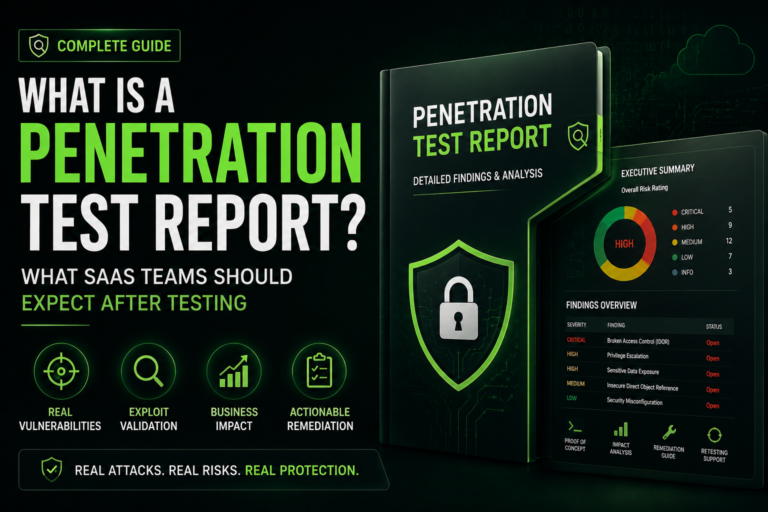
Title card: What Is a Penetration Test Report. A report cover beside an executive summary with a risk rating chart and a table of findingsFundamentals
Pentesting Guides7 min read

What Is a Penetration Test Report? What SaaS Teams Should Expect After Testing

Most companies think the penetration test is the final deliverable. It’s not. The real value often comes after the testing is complete: inside the penetration test report itself. Because a good penetration test report does more than list vulnerabilities. It explains how your application can actually be attacked, what business risk exists, how the issue\u{2026}

Key takeawayWhat separates a report your developers can act on from a tool export with severity labels attached.
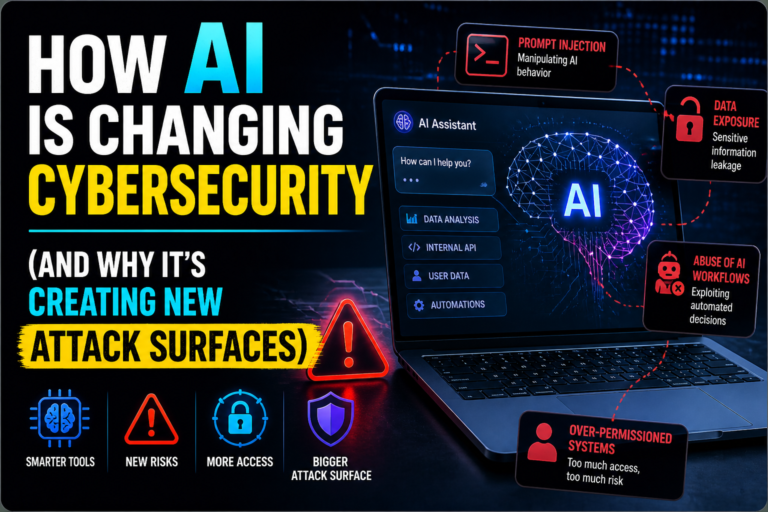
Title card: How AI Is Changing Cybersecurity. A laptop running an AI assistant, surrounded by warnings for prompt injection, data exposure and excessive permissionsFundamentals
AI Security4 min read

How AI Is Changing Cybersecurity (And Why It’s Creating New Attack Surfaces)

Artificial intelligence is quickly becoming a core part of modern applications. From chatbots and recommendation systems to internal automation tools and AI-powered workflows, SaaS platforms are integrating AI at an increasing pace. But while AI is improving efficiency and user experience, it is also introducing something most teams are not fully prepared for. New attack\u{2026}

Key takeawayAdding AI to a product adds inputs you do not control and permissions you did not audit.
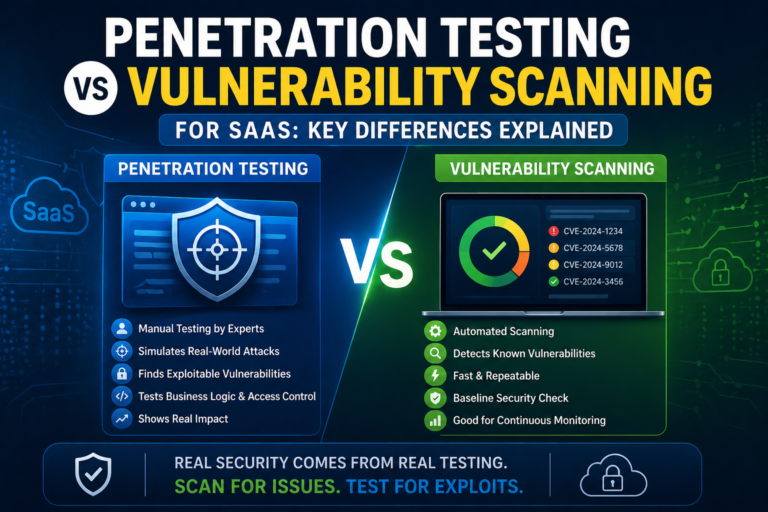
Comparison graphic: manual penetration testing that finds exploitable access control and logic flaws, beside automated vulnerability scanning that lists known CVEsFundamentals
Pentesting Guides5 min read

Penetration Testing vs Vulnerability Scanning (What Actually Finds Real Risks in SaaS Applications)

If you’re building a SaaS product or managing a web application, you’ve probably come across both terms: penetration testing and vulnerability scanning. They’re often used interchangeably, but in reality, they solve very different problems. Understanding that difference is critical, because choosing the wrong approach can leave real vulnerabilities completely unnoticed. What Vulnerability Scanning Does Vulnerability\u{2026}

Key takeawayDetection versus exploitation, what each one genuinely finds, and how often you actually need either.
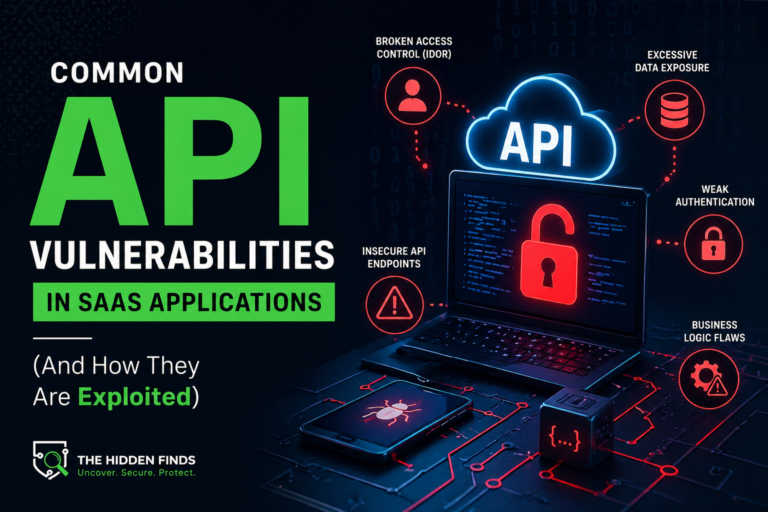
Title card: Common API Vulnerabilities in SaaS Applications. A laptop with an open red padlock under an API cloud, surrounded by vulnerability labelsPractitioner
API Security6 min read

Common API Vulnerabilities in SaaS Applications (And How They Are Exploited)

APIs are the backbone of modern SaaS applications. Every login, dashboard update, integration, or workflow is powered by API calls running in the background. But here’s the problem. Most SaaS companies focus heavily on the frontend and assume the backend APIs are “safe by default.” They’re not. In real-world security testing, APIs are often the\u{2026}

Key takeawaySeven API flaw classes with how each is exploited in practice, and why the API is the largest surface you own.
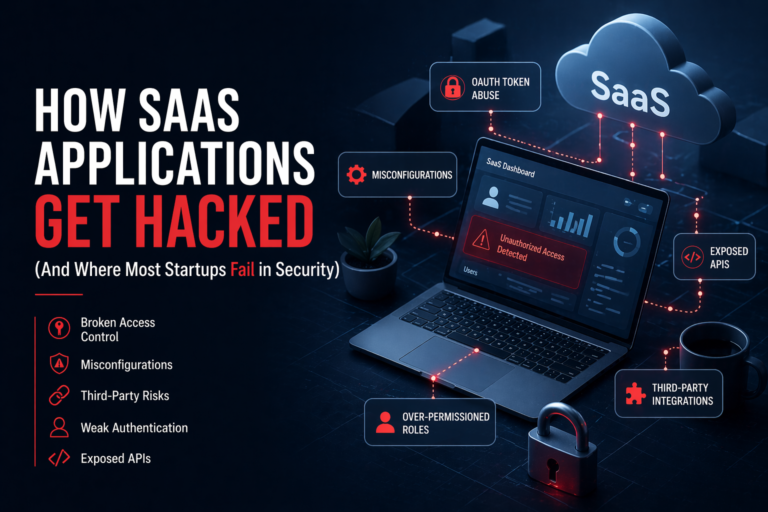
Title card: How SaaS Applications Get Hacked. A SaaS dashboard showing an unauthorized access alert, linked to token abuse, misconfigurations and exposed APIsFundamentals
SaaS Security4 min read

How SaaS Applications Get Hacked (And Where Most Startups Fail in Security)

Introduction Most SaaS companies believe they are secure. They rely on cloud infrastructure, managed services, and modern frameworks. On the surface, everything looks solid. But in reality, most breaches today don’t come from complex exploits or zero-days. They happen because of something much simpler: Access. Trust. And broken logic. In many cases, attackers don’t “hack”\u{2026}

Key takeawayMost breaches are not zero days. They are ordinary logic and access mistakes in software that looks well built.
The Hidden Finds, Security Beyond the Surface, written over a blue security dashboard with a magnifying glassFundamentals
Pentesting Guides4 min read

What Is The Hidden Finds? A Cybersecurity Company for SaaS Security, Penetration Testing & Vulnerability Assessment

If you have come across The Hidden Finds and are wondering what it actually is, this article is for you. In simple words, The Hidden Finds is a cybersecurity company that helps businesses find security weaknesses before attackers do. I work with modern companies, especially SaaS platforms and online businesses, to improve their security through\u{2026}

Key takeawayWhat the practice covers, how the work is done manually, and where the name comes from.
Title card: The Biggest Security Gap in SaaS: Asset Visibility. A laptop running a radar scan, surrounded by cloud services, folders and serversFundamentals
Asset Monitoring4 min read

What Is Asset Visibility in Cybersecurity (And Why It Matters for SaaS)

Most companies don’t get hacked because of advanced exploits. They get breached because of something much simpler: They don’t know what they have exposed. In modern SaaS environments, infrastructure changes constantly: Over time, visibility breaks. That’s where the real risk starts. The Problem No One Talks About Security teams invest in: But they often miss\u{2026}

Key takeawayAsset detection finds what is exposed. Visibility means knowing it is yours, who owns it, and whether it should exist.
Reading path

Access control, start to finish

Four articles that build on each other, from what the flaw is through to how to test for it. Read them in this order if the subject is new to you.

  1. 01 Broken access control
  2. 02 IDOR explained
  3. 03 Authorization testing guide
  4. 04 Access control checklist
SECURITY INSIGHTS

Stay Updated

Explore new security research, attack-path analysis, and practical SaaS security insights.