What Is a Penetration Test Report? What SaaS Teams Should Expect After Testing
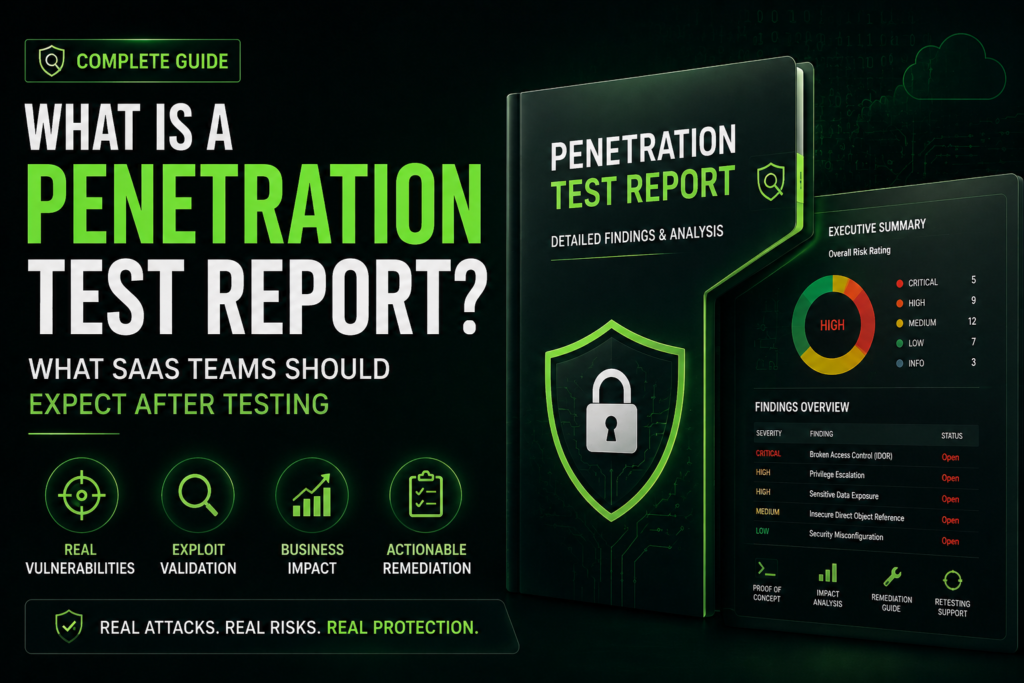
Most companies think the penetration test is the final deliverable. It’s not. The real value often comes after the testing is complete: inside the penetration test report itself. Because a good penetration test report does more than list vulnerabilities. It explains how your application can actually be attacked, what business risk exists, how the issue […]
Penetration Testing vs Vulnerability Scanning (What Actually Finds Real Risks in SaaS Applications)
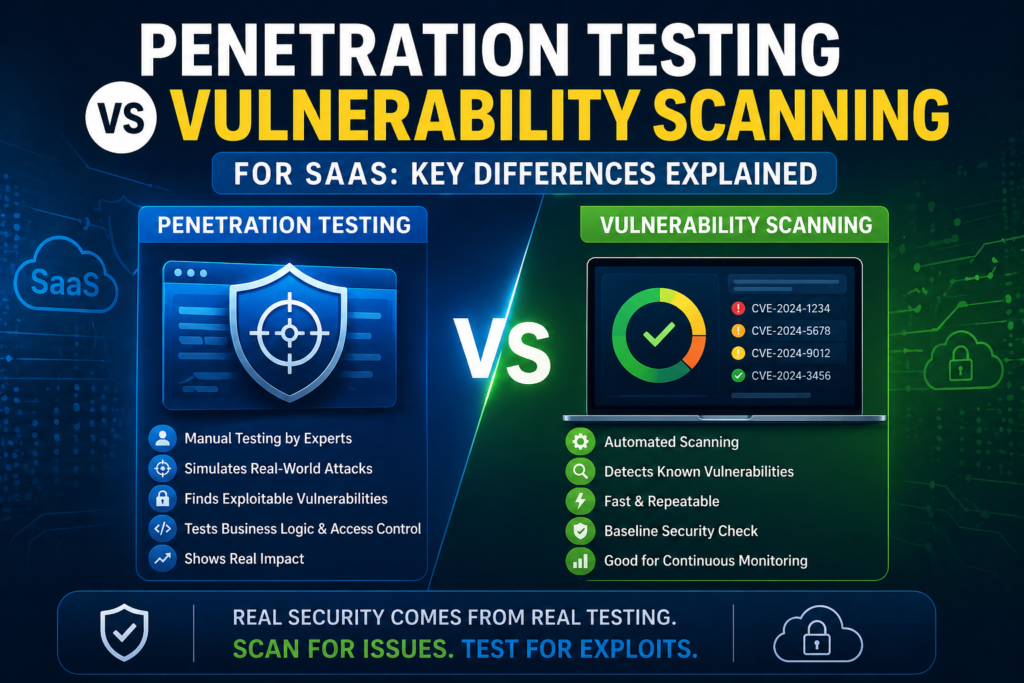
If you’re building a SaaS product or managing a web application, you’ve probably come across both terms: penetration testing and vulnerability scanning. They’re often used interchangeably, but in reality, they solve very different problems. Understanding that difference is critical, because choosing the wrong approach can leave real vulnerabilities completely unnoticed. Vulnerability scanning is an automated […]
How SaaS Applications Get Hacked (And Where Most Startups Fail in Security)
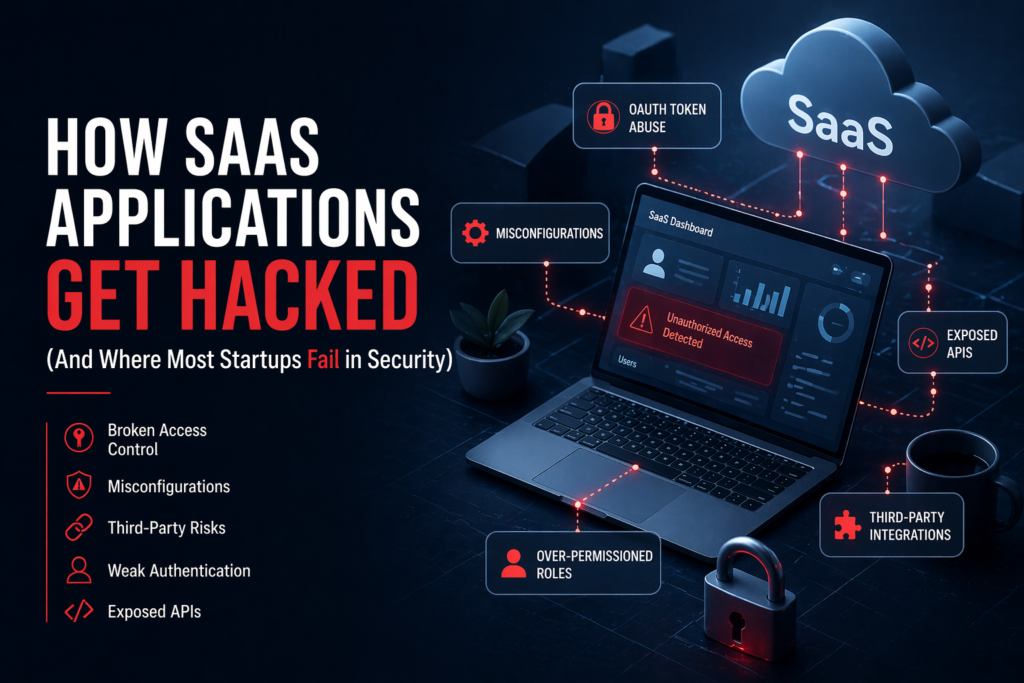
Introduction Most SaaS companies believe they are secure. They rely on cloud infrastructure, managed services, and modern frameworks. On the surface, everything looks solid. But in reality, most breaches today don’t come from complex exploits or zero-days. They happen because of something much simpler: Access. Trust. And broken logic. In many cases, attackers don’t “hack” […]
What Is The Hidden Finds? A Cybersecurity Company for SaaS Security, Penetration Testing & Vulnerability Assessment
If you have come across The Hidden Finds and are wondering what it actually is, this article is for you. In simple words, The Hidden Finds is a cybersecurity company that helps businesses find security weaknesses before attackers do. We work with modern companies, especially SaaS platforms and online businesses, to improve their security through […]