Artificial intelligence is quickly becoming a core part of modern applications. From chatbots and recommendation systems to internal automation tools and AI-powered workflows, SaaS platforms are integrating AI at an increasing pace.
But while AI is improving efficiency and user experience, it is also introducing something most teams are not fully prepared for. New attack surfaces.
The problem is not that AI is insecure by default. The problem is that it changes how systems behave, how data flows, and how decisions are made. And in doing so, it creates entirely new ways for attackers to interact with applications.
AI Is Expanding the Attack Surface
In traditional applications, the attack surface is relatively predictable. You have endpoints, authentication systems, APIs, and business logic. Security testing focuses on how these components behave under different conditions. AI changes this model.
Now you have systems that:
- Process untrusted input in dynamic ways
- Generate responses based on context
- Interact with external tools and data sources
- Make decisions without strict, predefined logic
This creates a layer of unpredictability that attackers can exploit. Instead of targeting fixed endpoints, attackers can now influence how the system thinks and responds.
Prompt Injection and Indirect Input Manipulation
One of the most common emerging issues is prompt injection. In simple terms, attackers manipulate the input given to an AI system in order to change its behavior.
For example, if an AI assistant is designed to retrieve and summarize internal data, an attacker may craft input that forces the LLM to expose information it should not reveal.
This becomes more dangerous when AI systems are connected to:
- Internal APIs
- Databases
- External integrations
Because now the AI is not just responding. It is acting.
Over-Permissioned AI Systems
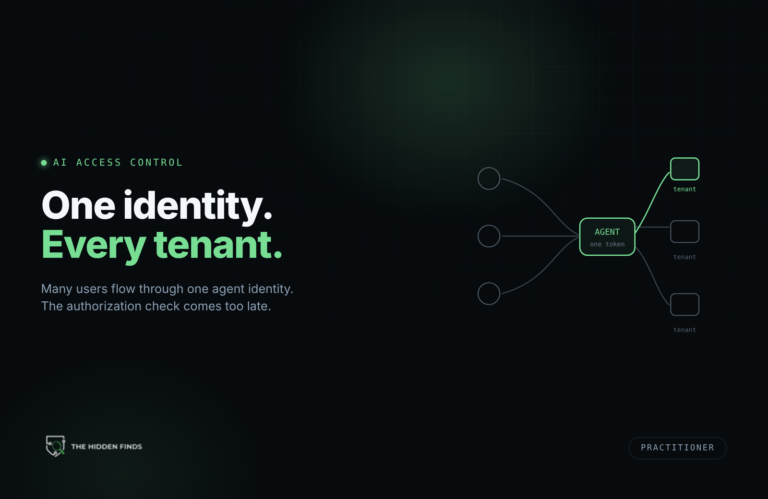
Many AI integrations are given broad access to systems to make them useful.
This includes:
- Access to user data
- API permissions
- Internal tools
- Automation capabilities
If these permissions are not tightly controlled, the AI becomes a high-value target.
An attacker who can influence or abuse the AI system may be able to:
- Access sensitive data
- Trigger unintended actions
- Escalate privileges
This is similar to traditional access control issues, but amplified by automation. The risk grows again once an AI system can take actions on its own, which I cover in AI agent security risks in SaaS.
Data Leakage and Workflow Abuse
AI can leak data while appearing to work correctly, because under certain inputs a response may reveal internal information or system behavior it was never meant to share. As AI takes on more of the workflow, approving requests, automating tasks and feeding outputs into other systems, an attacker who shapes its input can also bypass controls or trigger actions nobody intended. I cover both risks in more detail in data leakage and decisions built on AI output.
Why Traditional Security Testing Falls Short
Most security testing approaches are not designed for AI-driven systems.
Automated scanners cannot:
- Understand prompt behavior
- Evaluate AI decision-making
- Detect indirect manipulation
- Identify logic abuse in AI workflows
Even traditional penetration testing needs to adapt.
Testing AI systems requires:
- Understanding how the model interacts with inputs
- Evaluating integrations and permissions
- Simulating real misuse scenarios
What This Means for SaaS Security
For SaaS platforms, this shift is significant. AI is not just another feature. It becomes part of the core application logic.
Which means:
- It must be treated as part of the attack surface
- It must be tested like any other critical component
- It must be controlled and monitored carefully
Ignoring this layer can introduce risks that are difficult to detect and even harder to fix later.
Final Thoughts
AI is changing cybersecurity, but not just by improving defenses. It is also creating new opportunities for attackers. The systems are more dynamic, more connected, and more powerful, which makes them more valuable targets.
Understanding how AI can be abused is now just as important as understanding traditional vulnerabilities.
Because the question is no longer just: “Is the system secure?”
It is: “How can this system be influenced, manipulated, or misused?”